📊 Full opportunity report: Friendly Fire At Alliance Scale: What Chinese Equipment In NATO Networks Actually Means on ThorstenMeyerAI.com — validation score, market gap, and execution plan.

Get business pricing on tech for your team
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
TL;DR
NATO’s critical communication networks are heavily dependent on Chinese-made equipment, which legally obligates companies to cooperate with Chinese intelligence. This dependency raises concerns about potential security breaches and friendly fire risks, though no breaches have been publicly confirmed.
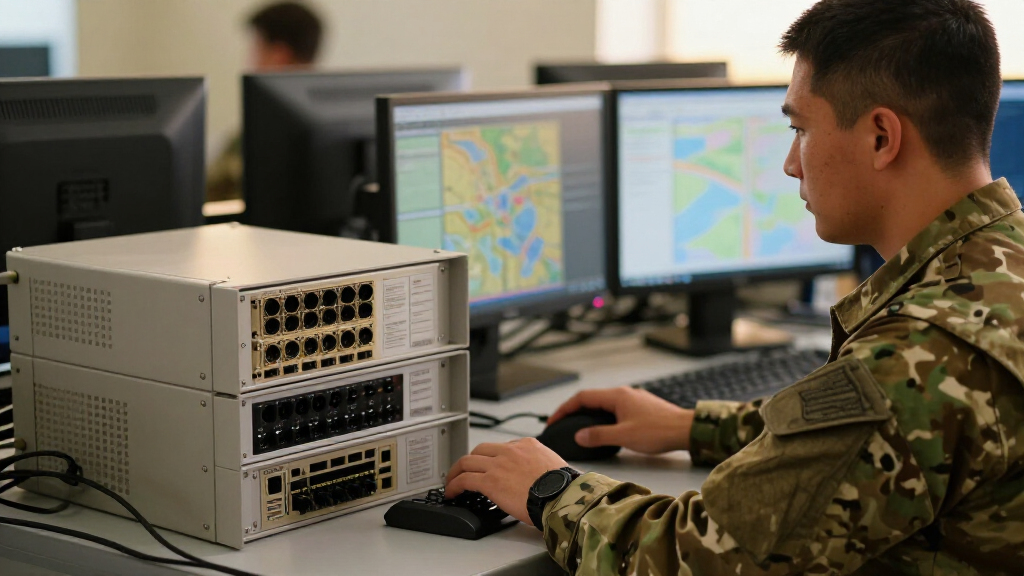
NATO’s critical communication networks and sensor systems are heavily reliant on equipment sourced from China, raising concerns over potential security vulnerabilities. This dependency stems from longstanding procurement practices, and the legal obligations imposed by Chinese law could, in theory, enable Beijing to access or disrupt NATO systems, though no such breach has been publicly confirmed. The development underscores the alliance’s strategic vulnerabilities and the ongoing efforts to replace Chinese technology.
Multiple NATO member states, including Belgium and Germany, have significant portions of their telecommunications infrastructure built on Chinese equipment, primarily Huawei. Belgium’s EU and NATO communications infrastructure, until recently, depended on Chinese technology, which is subject to China’s National Intelligence Law of 2017, mandating cooperation with Chinese intelligence agencies. Germany’s 5G network relies on Huawei for approximately 60% of its radio access network, with major operators seeking to replace or upgrade these components amid security concerns. Eastern European countries bordering Russia and Belarus also maintain Chinese-built networks, with no immediate plans for removal.
Despite Chinese firms denying backdoor access or illegal cooperation, the legal framework allows the Chinese government to instruct companies like Huawei and DJI to provide intelligence or disrupt services if ordered. The alliance’s security measures are increasingly focused on replacing Chinese gear, with deadlines set for 2026 in Germany and ongoing efforts across Europe. However, the technical and financial challenges of complete removal remain significant, and no documented breaches have been publicly confirmed to date.
Friendly fire at alliance scale: what Chinese equipment in NATO networks actually means
Yesterday: Ukraine may have turned a Russian unit’s identification layer against its own jet. Today’s question doesn’t require that to be true. It requires only that the concept be plausible — and then asks what it means when NATO’s own identification layer is built on equipment from a country whose law compels its companies to cooperate with intelligence on demand.
Any Chinese entity — any company, any employee, anywhere — must assist national intelligence work when asked. No carve-out for foreign deployments. No judicial review. No refusal option. When Beijing asks Huawei for access, Huawei must provide it. The law doesn’t distinguish between Shenzhen and Stuttgart. It doesn’t distinguish between civilian and NATO. This is not theoretical. It is operational law.
Requires no reconnaissance. The companies manufactured and installed the equipment. They have the source code, firmware, manufacturing tolerances, and update pipeline — the reconnaissance was completed before the adversary was even identified as one. A stronger position than what InformNapalm claims Ukraine achieved.
The question isn’t whether China will use this access. It’s whether NATO can afford to assume it won’t. Three things follow. Replacement is genuinely hard — banning without building the supply chain produces capability gaps, not security. The identification layer is where the exposure is sharpest — a Chinese motor is a supply-chain risk; a Chinese sensor or processor in an IFF system is an identification-layer risk, the same class the BARS Moscow story made visible. And the open-weight argument applies here — but stops short: open weights give you visibility into the classification model; they don’t give you visibility into the silicon it runs on. NATO has thirty-two members, each with its own procurement history. Together they’ve built an identification layer with distributed, unaudited, legally-accessible dependencies on a potential adversary. BARS Moscow required weeks of reconnaissance. The reconnaissance for NATO’s version was completed in the factory.
Potential Impact of Chinese Equipment on NATO Security
This dependency on Chinese equipment in NATO’s communication and sensor networks presents a strategic vulnerability. If Beijing were to issue directives to Huawei or other Chinese firms, it could theoretically enable espionage, data manipulation, or even disruption of military communications during a conflict. While no breaches have been publicly confirmed, the legal obligations under Chinese law mean the risk is structural and legal, not just technical. This situation could compromise alliance cohesion and operational security, especially in a future conflict involving China or its allies.
As an affiliate, we earn on qualifying purchases.
Historical Dependence and Ongoing Security Concerns
Over the past decade, NATO countries have increasingly relied on Chinese telecommunications equipment due to cost and technological factors. Belgium and Germany are among the most affected, with Chinese gear forming a significant part of their mobile networks. The U.S. and other allies have repeatedly urged NATO members to replace or upgrade these systems, citing potential security risks. The 2017 Chinese National Intelligence Law explicitly requires companies to cooperate with Chinese intelligence, creating a legal backdoor that can be exploited during crises. NATO’s efforts to diversify and secure its networks are ongoing but face technical, logistical, and financial hurdles.
Recent assessments indicate that, while no confirmed breaches have occurred, the legal framework and dependency create a plausible risk of exploitation, especially in high-tension scenarios involving China or its allies.
NATO communication security devices
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Unconfirmed Risks and Lack of Documented Breaches
While the legal and structural risks are clear, there have been no publicly confirmed cases of Chinese equipment being exploited to conduct espionage or disrupt NATO operations. It remains uncertain whether Beijing has actively used this legal obligation to access or manipulate NATO systems during a conflict. The actual level of vulnerability and the likelihood of exploitation under current conditions are still under assessment.
As an affiliate, we earn on qualifying purchases.
NATO’s Strategic Plans for Network Security and Replacement
NATO is actively working to replace Chinese equipment in its networks, with deadlines set for 2026 in key countries like Germany. The alliance is also exploring technical solutions to mitigate vulnerabilities, including hardware upgrades and network segmentation. Continued assessments and transparency about risks and progress are expected over the coming months, alongside diplomatic efforts to coordinate the removal of untrusted vendors.
secure military communication equipment
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Key Questions
What specific Chinese equipment does NATO rely on?
The most significant reliance is on Huawei’s 5G radio access network components, which carry a large portion of mobile traffic in Germany and other European countries. Belgium’s communications infrastructure also includes Chinese equipment used by NATO and EU institutions.
Has there been any confirmed breach involving Chinese equipment in NATO?
No publicly confirmed breaches have been reported. While the legal framework could enable exploitation, no incidents have been publicly documented.
What are NATO’s plans to address this dependency?
NATO countries are working to replace Chinese equipment, with deadlines such as 2026 in Germany. Efforts include technical upgrades, policy measures, and seeking alternative vendors to reduce reliance on Chinese technology.
Could this dependency lead to a friendly fire incident?
While technically possible if adversaries exploit the vulnerabilities, there is no evidence this has occurred. The primary concern is the potential for espionage or disruption during a conflict.
Source: ThorstenMeyerAI.com
Halloween Picks
halloween
As an affiliate, we earn on qualifying purchases.