TL;DR
The Pragmatic Engineer published an interview with Antithesis distinguished engineer Sean Allen about software correctness and reducing defects. Allen discusses preventing invalid states through language design and testing repeated workloads, and says there is no simple defense against software supply-chain attacks.
The Pragmatic Engineer has published an interview with Sean Allen, a distinguished engineer at Antithesis, about software correctness and supply-chain risks. Allen discusses defining what a program must guarantee and says tests or late-stage quality gates alone may not address every defect.

Get business pricing on tech for your team
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
Allen describes software correctness in terms of whether a program does what people expect, using invariants—formal guarantees about behavior—as a way to specify those expectations. He also points to a practical difficulty: teams may recognize when software fails without having clearly defined what success should look like beforehand. In his words, software is “correct enough” when it serves its business purpose and does not cause an overnight outage.
The discussion challenges the idea that testing should be the main safeguard. Allen favors designing systems so that illegal states cannot be expressed in the first place, including through languages with strong type systems. He also describes repeated, realistic workloads as a way to examine system behavior beyond isolated unit tests. One example mentioned in the article is the Bank Test, used to stress-test database isolation guarantees.
On supply-chain security, Allen says package hijacking is difficult to prevent because malicious code can run when a compromised dependency is installed or used. He argues that languages designed with strong security protections, such as E, have not become widely adopted, while popular languages often rely on an ecosystem being trustworthy. The article presents this as Allen’s assessment, not as a claim that every package or language is unsafe.
Correctness Before Code Ships
The interview addresses challenges engineering teams face when defining requirements and assumptions about component behavior. Allen discusses invariants and workload-based checks as ways to specify expected behavior and examine systems under repeated conditions.
Allen also discusses the risks associated with external software packages. A compromised dependency can expose systems to malicious code. He does not propose a universal technical remedy; the interview presents quality and dependency risk as topics requiring continued attention, rather than matters resolved by a single test or approval step.
Products Worth Considering
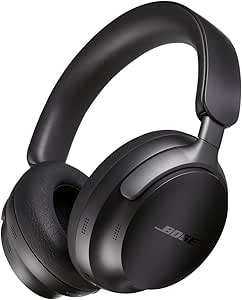
Bose QuietComfort Ultra Wireless Over-Ear Headphones with Spatial Audio and Noise Cancellation, Black

Bose QuietComfort True Wireless Earbuds with Active Noise Cancellation, Bluetooth 5.3, USB-C Charging, and IPX4 Water Resistance

Bose QuietComfort Wireless Noise-Cancelling Over-Ear Headphones, Twilight Blue
As an affiliate, we earn on qualifying purchases.
Allen’s Engineering Background
Allen works on software correctness at Antithesis and has experience with large distributed systems, stream processing and confidential computing. He is also a core contributor to Pony, a programming language designed for concurrency. The interview draws on that experience to discuss language design, runtime performance and how systems can be built to behave predictably.
The Pragmatic Engineer says the conversation was motivated by interest in correctness as software production accelerates. Its editor also disclosed that Antithesis sponsors the publication’s podcast, while stating that the interview itself was not sponsored by the company. The source additionally announced The Pragmatic Summit, scheduled for Feb. 10 in San Francisco, but that event is separate from the interview’s technical discussion.
““It’s down to whether my program does what I expect.””
— Sean Allen, distinguished engineer at Antithesis
Limits of the Interview’s Claims
The source is an interview and does not report a new security incident, a measured test of Allen’s recommendations or comparative data on defect rates across programming languages. It does not quantify how much workload-based testing improves reliability, or specify which languages or organizational controls would best reduce package compromise risk.
Allen’s statements about language adoption and supply-chain defenses are his analysis. The material does not establish that strong type systems prevent all defects, that testing is unnecessary, or that any one approach can prevent dependency attacks. The interview also does not provide a detailed security checklist or a new product announcement from Antithesis.
Applying the Advice in Practice
The interview sets out engineering principles rather than a scheduled technical release or policy change. Teams applying Allen’s ideas would need to define the invariants relevant to their systems, decide which workloads can test those guarantees repeatedly, and assess how they manage third-party dependencies.
No follow-up study, product launch or additional milestone is specified in the source. The Pragmatic Engineer says readers can watch the conversation on YouTube; further reporting would be needed to assess how the proposed practices perform across different systems and teams.
Key Questions
What does Sean Allen mean by software correctness?
He defines it as whether a program does what is expected. He frames those expectations as invariants, or guarantees about software behavior.
Does Allen argue that teams should stop testing?
No. The interview says he is skeptical of manual testing as the primary way to ensure correctness. He emphasizes preventing invalid states through design and checking systems with repeated workloads.
What is the Bank Test mentioned in the interview?
The article identifies it as an example of a workload used to stress-test database isolation guarantees. It does not give a full test procedure.
What is Allen’s concern about software supply chains?
A hijacked package can introduce malicious code that runs on a machine or service. Allen says there is no single or simple fix, citing a tension between secure language designs and the popularity of languages that rely on a trustworthy ecosystem.
Was the interview sponsored by Antithesis?
The Pragmatic Engineer says Antithesis sponsors its podcast but that this interview was not sponsored by the company.
Source: newsletter.pragmaticengineer.com